


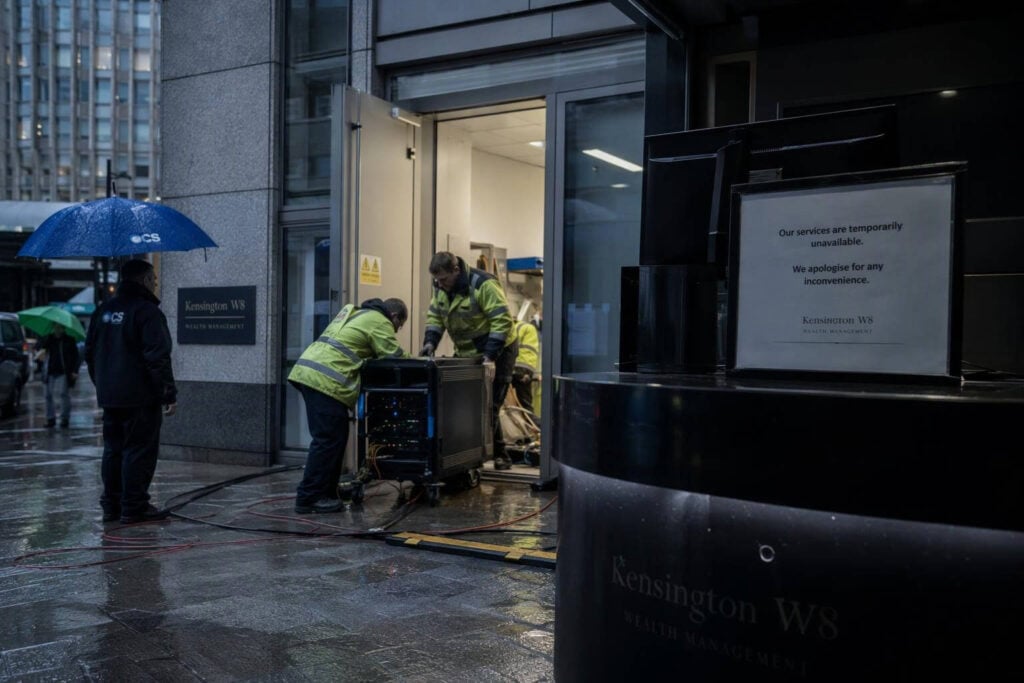


The Saltus cyber attack reportedly exposed data relating to almost 100 clients and forced the UK wealth manager’s client portal offline. The incident was first reported publicly on 6 November 2026, although significant technical and operational details remain undisclosed.
The portal was accessible when checked later on 6 November, suggesting that the reported disruption was temporary, partial or resolved before that observation. Saltus had not published a public incident statement on its media page as of the same date.
What happened in the Saltus cyber attack?
Citywire reported that Saltus suffered a cyber attack during the weekend before 6 November 2026. According to the report, the incident caused the wealth manager’s client portal to be taken offline and exposed data associated with almost 100 clients.
This represents a reported, real-world compromise rather than the discovery of a theoretical vulnerability. However, no information has been published about how attackers obtained access, how long they may have remained inside the environment or whether the portal itself was the original entry point.
The principal facts reported so far are:
- Saltus, a UK wealth manager, was reportedly targeted during the weekend before 6 November 2026.
- Data relating to almost 100 clients was reportedly exposed.
- The Saltus client portal was taken offline because of the incident.
- The portal was subsequently accessible when checked on 6 November 2026.
- No threat actor, malware family or initial access technique has been identified publicly.
It is also not clear whether taking the portal offline was a precautionary containment measure or the direct result of technical disruption. Temporarily disabling an online service can help an organisation prevent further access while investigators examine logs, accounts, systems and possible data loss.
Saltus cyber attack timeline and portal status
Attack reported over the preceding weekend
The attack reportedly occurred during the weekend before Friday, 6 November 2026. No more precise date or time has been made public, so the duration of the compromise and the length of the portal outage cannot currently be established.
There is also no confirmed timeline showing when Saltus detected the incident, when containment began or when affected clients were informed. Those details would be important for understanding the speed of the response, but they were not included in the material available.
Incident became public on 6 November
Citywire first reported the Saltus cyber attack on 6 November 2026. At that point, the report said the client portal had been forced offline and that data concerning almost 100 clients had been exposed.
No independent news report confirming the core incident details was identified during the subsequent research. No public statement or customer-facing cyber incident advisory was found on the Saltus media page as of 6 November either. This does not establish that no private notifications were issued, only that no relevant public notice was visible.
Client portal observed online
The Saltus portal at clientportal.saltus.co.uk was reachable when checked on 6 November 2026. It displayed a login page carrying the version number 2.16.0, indicating that at least the public login service was available at the time of observation.
This does not necessarily contradict the report that the portal had been taken offline. The service may have been restored before it was checked, the outage may have affected only certain users or functions, or Saltus may have moved the public login page to a clean environment. Without an official technical account, the reason cannot be confirmed.
Affected system, version and exposed data
The only specifically identified system is the Saltus client portal. Its public hostname is clientportal.saltus.co.uk, and the login page displayed version 2.16.0 when observed on 6 November 2026.
That version string should not be interpreted as confirmation of a vulnerable software release. The portal’s underlying platform, hosting provider, application framework and supporting technology have not been publicly disclosed. There is no published evidence linking version 2.16.0 to a known flaw or showing that exploitation of the portal software caused the incident.
Citywire reported that data relating to almost 100 clients was exposed, but the types of information involved have not been specified. It is therefore unknown whether the affected material included identity details, contact information, account records, financial documents, authentication data or another category of information.
No public account has explained whether the data was viewed, copied or transferred outside the Saltus environment. There is also no credible public evidence of the information appearing on a criminal leak site. The word exposed should consequently be understood in the limited context of the original report, not as confirmation of public release.
Attack method and current exploitation status
No initial access vector has been disclosed for the Saltus cyber attack. There is no confirmed connection to phishing, stolen credentials, an unpatched vulnerability, a supplier compromise or malicious activity by an insider.
No threat actor has claimed responsibility publicly through a source considered credible in the available research. There are also no published indicators of compromise, such as malicious IP addresses, domains, file hashes or filenames, that other organisations can use to search their systems for related activity.
The incident itself is evidence of in-the-wild malicious activity against Saltus, based on Citywire’s report. It is not, however, evidence of a broader exploitation campaign against a particular product. No proof of concept, vulnerability identifier or affected product range has been associated with the event.
Several important questions therefore remain unanswered:
- How the attackers first entered the environment.
- Whether the client portal was compromised directly or disabled as a precaution.
- Which categories of client data were exposed.
- Whether information was removed from Saltus systems.
- How long unauthorised access may have continued.
- Whether any third-party service or supplier was involved.
Why the Saltus incident matters
The Saltus cyber attack demonstrates the combined operational and information risks surrounding online client services. A portal can become unavailable during containment even when it is not the original route used by an attacker, leaving clients without normal access while the organisation investigates.
The limited public information also creates uncertainty for clients, employees and business partners. When an early media report precedes an official advisory, organisations need to assess what is confirmed, avoid speculation and prepare accurate updates as facts emerge.
What organisations should do now
Organisations operating comparable portals should review whether they can rapidly isolate a service without losing essential forensic evidence. Restoration plans should cover clean deployment, account and session revocation, log preservation, security testing and checks that connected systems have not also been affected.
- Confirm that portal, identity and administrative logs are retained for an adequate investigation period.
- Test procedures for disabling and restoring client-facing applications safely.
- Prepare communications for service disruption and potential data exposure.
- Define how affected individuals, regulators and other stakeholders will be notified when required.
- Monitor for verified statements that clarify the attack method, exposed data and scope.
Further clarity will depend on an official Saltus statement, a regulator notice or corroborated reporting. Until then, version 2.16.0 should not be treated as vulnerable, and unconfirmed claims about attackers or stolen data should be approached cautiously.
Originally reported by Citywire.

