

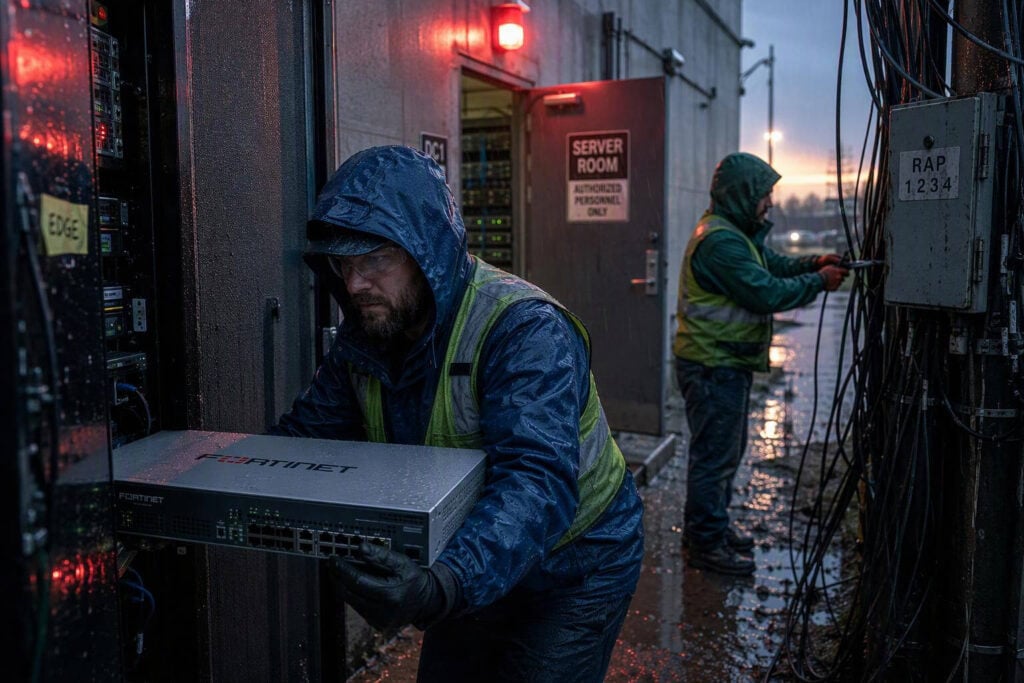


The FortiBleed campaign remains active, with attackers using compromised credentials to access Fortinet firewalls and VPN gateways. A US government alert warns that intruders can lock legitimate owners out and provide access to ransomware operators, while a researcher says they can create administrator accounts.
The FBI and US Secret Service published the industry alert on 6 October 2026. It confirms that FortiBleed is not simply a historical credential leak, but an ongoing operation affecting internet-facing FortiGate firewalls and FortiOS SSL VPN gateways.
FortiBleed campaign prompts new government alert
The 6 October alert, titled “FortiBleed Operations Continue Targeting Exposed Systems Leading to Reports of Lockouts”, says affected organisations may lose access when attackers disable accounts or change passwords. Recovering control can therefore require more than installing updates or resetting a single password.
Once authenticated, attackers can make administrative changes that preserve their access. These may include creating new privileged users, modifying existing accounts and changing device configurations. The FBI and US Secret Service also confirmed that FortiBleed access has been used as an entry point for ransomware affiliates.
INC and Lynx ransomware operations have been linked to access obtained through the campaign. The activity is assessed as financially motivated access brokering, in which one group compromises an organisation’s perimeter device and then supplies that foothold to another criminal operation.
The agencies are seeking indicators from affected organisations, including attacker-controlled IP addresses and unauthorised usernames. No authoritative public list of campaign IP addresses or file hashes was identified in the available government and vendor material, making organisation-specific investigation particularly important.
How the FortiBleed campaign developed
The operation became public months before the latest government warning. On 13 June 2026, security researcher Volodymyr “Bob” Diachenko reported an exposed FortiBleed dataset containing valid administrative and SSL VPN credentials associated with about 73,932 FortiGate URLs across 194 countries.
SOCRadar subsequently analysed the infrastructure and verified a database of 86,644 working device credentials. Its later investigation identified a much wider operation targeting more than 400,000 firewalls. These figures describe different stages of discovery, targeting and credential validation, so they should not be treated as directly comparable victim totals.
Key dates in the investigation
- 13 June 2026: The first public report described credentials for approximately 73,932 FortiGate URLs across 194 countries.
- 18 June 2026: CISA issued an alert about leaked credentials affecting approximately 74,000 Fortinet devices. The alert was revised on 22 June.
- 19 June 2026: Fortinet published its situational analysis, attributing initial access to credential reuse and brute-force activity rather than a new vulnerability.
- Late June to early July 2026: Independent reporting connected access from the operation to INC and Lynx ransomware activity.
- 6 October 2026: The FBI and US Secret Service confirmed that operations were continuing and that victims had reported device lockouts.
CyPro previously examined the initial credential exposure in its earlier FortiBleed campaign bulletin. The latest alert materially develops that story by confirming continued exploitation, administrative lockouts and ransomware-related access brokering.
Which Fortinet products are affected
The FortiBleed campaign targets internet-facing Fortinet FortiGate firewalls and FortiOS SSL VPN gateways. It is not tied to one product version or a single newly discovered CVE. Exposure instead depends on factors such as valid stolen credentials, password reuse, weak authentication and management or VPN services reachable from the internet.
Fortinet says attackers initially gained access by reusing credentials from previous compromises and conducting brute-force attempts against devices without effective multifactor authentication. This distinction matters because applying a software patch alone does not invalidate credentials that criminals already possess.
Fortinet has also highlighted credential storage improvements in the latest releases within FortiOS trains 7.4, 7.6 and 8.0. These releases support PBKDF2 hashing for administrator credentials, and the vendor recommends removing legacy password storage settings after upgrading and validating the configuration.
How attackers collect and reuse credentials
Researchers observed mass scanning of the FortiGate SSL VPN /remote/login endpoint during reconnaissance and credential-stuffing activity. Attackers could test previously obtained username and password combinations at scale, concentrating on gateways without MFA or with reused passwords.
Analysis also identified a custom Golang tool commonly called “FortigateSniffer” on compromised appliances. The tool abuses FortiOS’s legitimate diagnose sniffer packet function to passively inspect authentication traffic passing through a device.
This post-compromise capability helps explain why the operation is more serious than a static database of old passwords. A compromised firewall or VPN gateway sits at a sensitive network boundary, where captured traffic may expose credentials for VPN accounts, internal services or other systems.
Attackers can then reuse collected credentials, establish additional accounts and retain access even after an obvious password is changed. Where an access broker transfers control to a ransomware affiliate, the Fortinet appliance may become the starting point for internal reconnaissance, lateral movement and eventual ransomware deployment.
Signs requiring investigation
Fortinet guidance identifies several suspicious administrator names that organisations should check for, while recognising that attackers can select other names. Accounts requiring scrutiny include:
- forticloud
- fortiuser
- fortinet-support
- fortinet-tech-support
Security teams should also examine unexpected password changes, disabled legitimate accounts, newly created administrators, unusual remote logins and unexplained configuration changes. Logs should be reviewed for activity beyond the Fortinet device, particularly authentication to internal systems following suspicious VPN or administrative access.
What organisations using Fortinet should do
Organisations should treat exposed credentials as compromised even if their FortiGate device is fully patched. The immediate priority is to regain control of active sessions and remove any persistence created through unauthorised accounts or configuration changes.
- Terminate all active administrative and VPN sessions before rotating credentials.
- Reset every Fortinet administrative and VPN password, not only accounts known to have been exposed.
- Enforce MFA for all administrator and VPN accounts.
- Remove internet-accessible administration or restrict it to trusted management networks.
- Audit users, privileges and configurations for unauthorised additions or changes.
- Review logs for suspicious access and evidence of movement into internal systems.
- Upgrade to an appropriate current FortiOS release and disable legacy credential storage settings.
If administrators are already locked out, normal password rotation may be insufficient. Recovery should include controlled restoration of device access, validation of the full configuration and investigation of connected systems before the gateway is returned to normal operation.
The continuing FortiBleed campaign shows that remediation must address both the perimeter device and the credentials that passed through it. Organisations finding attacker IP addresses, usernames or related evidence should preserve the relevant logs and consider sharing those indicators with the appropriate authorities.
Originally reported by cyberscoop.com.

